Essential Eight · For Australian organisations
Independent Essential Eight assessment
Every control rated on evidence from your environment, with a costed plan to reach the level you have been asked for. Two to four weeks.
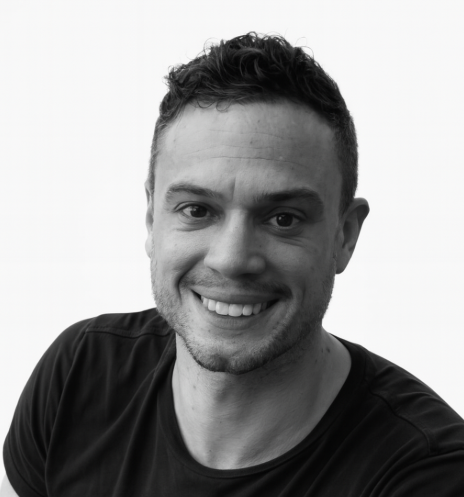
With Marcel Rizzolo, director. Typically A$12,000 to A$25,000 for a single-entity organisation; fixed quote in writing within one business day.- Every control rated on evidenceAgainst the current ASD Essential Eight Maturity Model
- Costed, sequenced uplift planEffort and cost against each step, ready for the board
- Independent of your MSPWe do not run your environment and the report goes to you
- Uplift by our engineers or your teamFollowed by a re-rating of the controls that were changed
What you get
Two to four weeks, four documents, one plan
Scoping call
Thirty minutes with Marcel. You tell us who is asking and by when. We confirm scope and send a fixed quote the next business day.
Evidence
We collect exports and screenshots from your environment with read-only access. Your IT team or MSP spends a few hours, not a few days.
Rating
Each control is rated against the current ASD maturity model. Aligned, partially aligned or open gap, with the evidence behind each call.
Report and plan
An executive brief, the full report, the workbook and policy recommendations. The uplift plan is costed and sequenced, ready for the board.
Most of the fixes sit in tools you already pay for. For Microsoft 365 that is Intune, Defender and Entra. Google Workspace and mixed estates are assessed the same way. Our engineers can do the uplift, or your own team can work from the plan. Either way we re-rate the controls once the work is done.
Already assessed, or know where you stand? If you have a recent assessment or MSP report and need help lifting your tools and processes to the next maturity level, or getting ready for ISO 27001, our uplift team can take it from there.
See Essential Eight upliftNext step
Book a free 30-minute consult
You will have a fixed quote in writing the next business day.
- No sales pitch. If an assessment is not what you need, Marcel will tell you on the call.
- Your details are used to set up the call and send the quote, nothing else.
Prefer email or phone? Send a note or call +61 2 7200 2554.
Who does the work
Assessed by people who have owned these controls
The practice
CISO-led
Our cyber security practice is led by our Chief Information Security Officer and run by Ben. The same team runs penetration testing, incident response and vCISO retainers.
The assessors
CISM and OSCP certified
Our assessors have led cyber consulting practices and held CISO and CTO roles in government and the private sector. The report is written by people who have run these controls.
The firm
Australian since 2010
Coder Trove has worked with mid-sized and enterprise organisations across Australia since 2010.
Our 2026 analysis of Australian breach costs sets out why insurers and regulators now ask to see the evidence.
Not ready to book?
See where you stand first
An indicative view of your position against each of the eight ASD strategies, and where you are most exposed. Two questions per strategy, about five minutes.
Eight strategies, two questions each
Answer for your organisation as it is today, not as the policy says it should be. Each section opens with why the strategy matters and one practical note from our assessors. Allow about five minutes.
At the end you see an indicative position for each strategy and overall. ASD scores an organisation at its weakest strategy, so one gap sets the level.
This quick assessment is a guide based on your answers. It is not a formal assessment and cannot be used as evidence for a client, insurer or Defence.
Common questions
Essential Eight assessment questions, answered
What does an Essential Eight assessment cost?
How long does it take?
Which maturity level do we need?
Is the assessment independent of our IT provider?
We run Google Workspace, not Microsoft 365. Can you still assess us?
Is this the same as an IRAP assessment?
Should we do the Essential Eight or ISO 27001 first?
ASD is replacing the Essential Eight. Should we still get assessed?
Can you deliver the uplift as well?
Related: Essential Eight quick check · Essential Eight uplift service · Essential Eight uplift guide · How the maturity model is scored · Essential Eight compliance checklist
Start here
Tell us who is asking, and by when
Thirty minutes with Marcel, then a fixed quote and a dated turnaround in writing the next business day.